
The product demonstration has gone well. The operations team likes the dashboard, the integrations appear compatible with existing systems, and the pricing falls within the approved budget.
Then the procurement manager raises a concern that wasn't part of the demonstration.
What happens to the company's data if the contract ends?
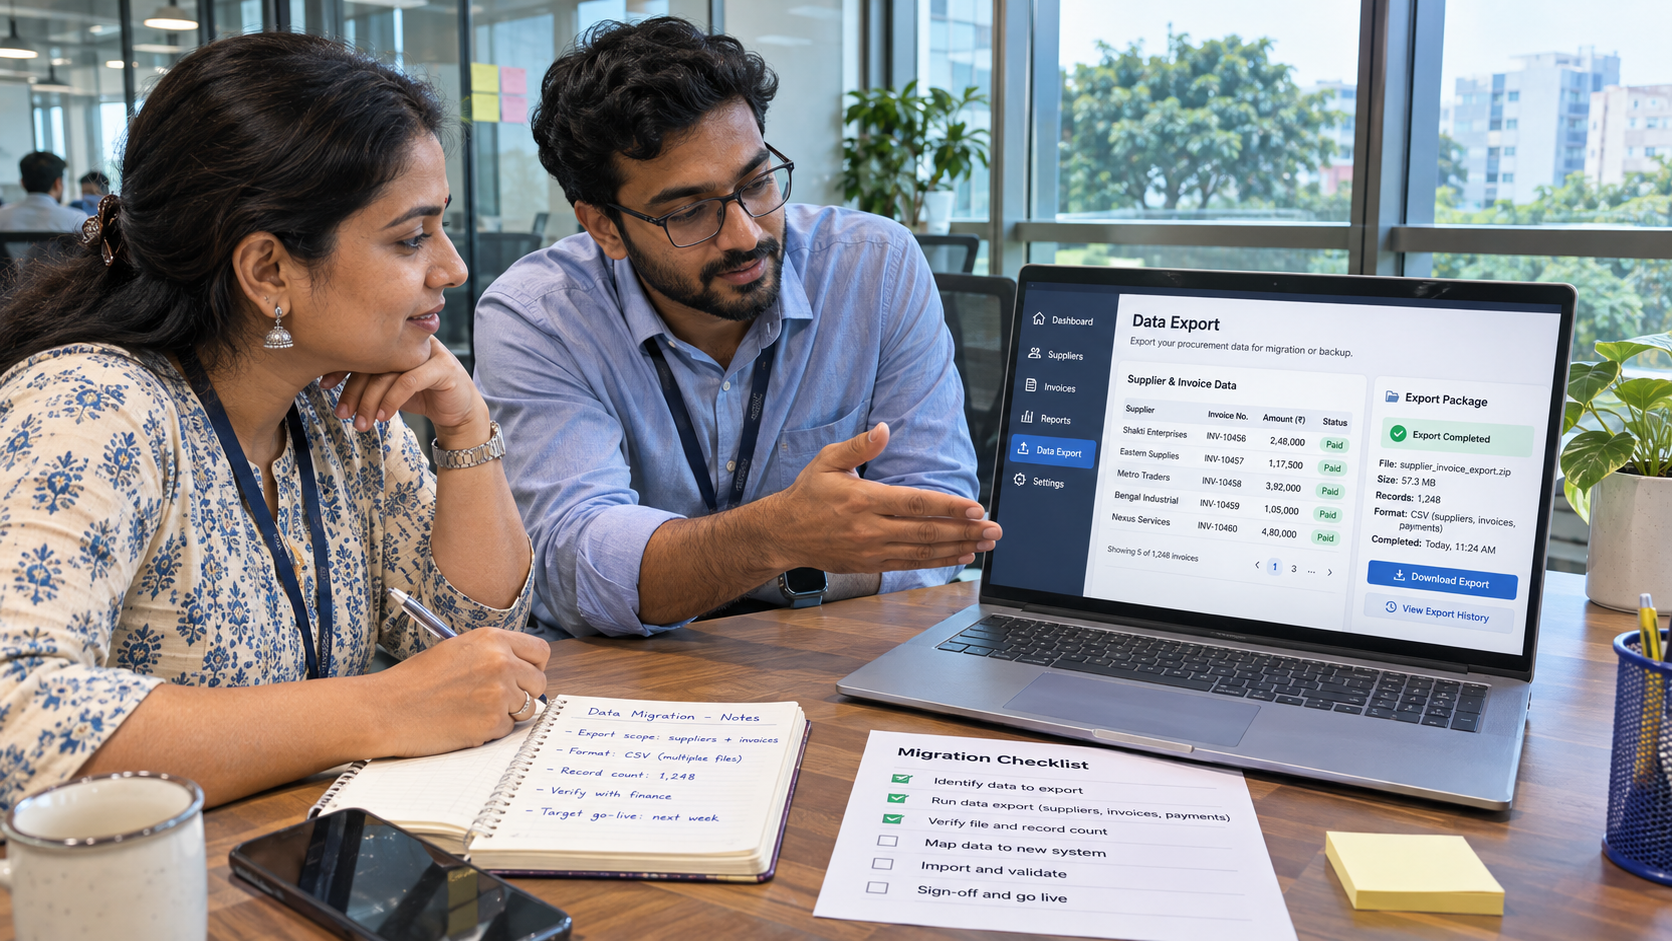
The SaaS provider explains that customers can download their records using the Export feature. That sounds reassuring until the IT team asks what the files actually contain.
Will the download include historical transactions, uploaded documents and approval records? Can those files be imported into another system without rebuilding the relationships between them? And who will help if the transfer fails?
These details can turn a straightforward software purchase into a lengthy technical and contractual review.
A SaaS platform may work exceptionally well while customers use it, but enterprise buyers also want confidence that important business information won't become inaccessible when they leave.
SaaS data portability is the ability to retrieve and transfer relevant customer data from a software platform in a usable, documented format, subject to applicable contractual and legal requirements. It helps businesses change providers or systems without unnecessarily losing access to the information they depend on.
Providing an Export button is a useful start. Whether the exported data is complete, understandable and suitable for migration is a different question.
Why Enterprise Buyers Are Asking About Data Before Signing
Consider a hypothetical company developing a SaaS platform for supplier management, purchase orders and invoice approvals.
The platform allows customers to maintain supplier profiles, create purchase orders, upload invoices and manage approvals. It also stores supporting documents and a history of completed transactions.
An enterprise customer plans to use the software across several departments.
Before signing, its procurement team wants to understand the exit arrangements. The company has previously experienced a difficult software migration and doesn't want to repeat it.
The SaaS provider says that customer information can be downloaded as CSV files.
The buyer asks for a sample export.
What arrives is a spreadsheet containing supplier names, contact details and purchase order numbers. The file opens correctly, but it doesn't include invoice attachments or approval history. The buyer also cannot determine which invoices belong to which purchase orders.
The provider has delivered data, but the customer still lacks much of the information required to move its operations elsewhere.
This is the distinction that matters during enterprise procurement. A platform should be able to explain not just what can be downloaded, but how that information remains useful once it leaves the original system.
Why a CSV Export May Not Be Enough
CSV and JSON are widely used formats for exchanging information. They can be suitable for SaaS exports, depending on the types of records involved.
The difficulty usually lies in the structure and completeness of the information rather than the file extension.
Suppose the supplier-management platform exports three datasets: suppliers, purchase orders and invoices.
The supplier file contains a unique ID for each business. Purchase orders reference those supplier IDs, while invoices reference their corresponding purchase orders.
If the export preserves those identifiers and documents their relationships, another system has a reasonable starting point for reconstructing the records.
If it replaces the identifiers with supplier names, deletes historical references or exports only the current status of each invoice, the receiving team may struggle to understand what happened.
The Relationships Between Records Matter
A purchase order isn't simply a row of information. It may have associated invoices, approved amounts, delivery records and supporting documents.
Those relationships need to survive the export if they form part of the agreed data scope.
The receiving system also needs to understand field meanings. An invoice marked "Approved" might mean it passed internal review, not that the supplier was paid.
Without documented definitions, another application could interpret the same record incorrectly.
This is why SaaS data portability should be considered during data-model design, not added as an afterthought when an enterprise customer requests an exit.
What a Usable SaaS Export Could Look Like
For the hypothetical supplier-management platform, the development team could define an export package containing structured records, attachments and documentation.
An illustrative package might include:
| Export Component | What It Contains |
|---|---|
| suppliers.csv | Supplier IDs and relevant supplier information |
| purchase_orders.csv | Order details, supplier references, amounts and statuses |
| invoices.csv | Invoice records and purchase-order references |
| approval_history.csv | Permitted approval events, timestamps and related record IDs |
| attachments/ | Relevant invoices, contracts and supporting documents |
| schema.json | Field definitions, data types and relationships |
| manifest.json | File inventory, record counts, checksums and export status |
This is an illustrative design, not a universal or legally prescribed SaaS export format.
The schema.json file explains how the information should be interpreted. The manifest helps the receiving team check which files and records were included, and whether the package changed during transfer.
For example, if the manifest lists 10,000 invoices but the exported invoice file contains only 9,970, the discrepancy can be investigated before the customer relies on the data.
Perhaps some records were deliberately excluded under an agreed scope. Perhaps the export failed while processing a batch. Either way, the system should make the difference visible rather than silently delivering an incomplete package.
The design of the export should reflect what customers are entitled to retrieve and what they actually need to do with the information.
Can an API Make Customer Data Easier to Move?
An API allows authorised software systems to exchange information programmatically.
For an enterprise customer, this can be useful when migrating records in stages or keeping two systems connected during a transition.
But an API isn't automatically a substitute for a complete export.
Some APIs expose current records but not historical changes. Others allow individual records to be retrieved but make bulk extraction difficult because of pagination, request limits or incomplete documentation.
The development team should therefore consider whether customers need both programmatic access and a bulk export facility.
A large customer may want to transfer historical records first, continue synchronising recent changes during migration and perform a final export before closing the old account.
That requires planning for record changes during the transition, not merely providing an endpoint that returns data.
Export Access Must Stay Within the Correct Customer Account
For a multi-tenant SaaS platform, data portability introduces a significant security responsibility.
The platform must verify who is requesting an export and which customer records that person is permitted to access.
An incorrectly implemented API could expose information belonging to another tenant if authorisation checks rely only on record IDs supplied in a request.
The OWASP API Security Top 10 identifies broken object-level authorisation as a major risk.
Export functions should enforce appropriate access controls, restrict downloads to authorised datasets and protect temporary export files. Sensitive exports may also require additional approval or verification, depending on the data involved.
Customers need a usable route out of the platform, but that route must not become a way to access someone else's information.
Who Owns the Data Stored in a SaaS Platform?
A SaaS contract should distinguish between customer data rights and the provider's intellectual property.
A customer may upload supplier details, purchase orders, invoices and other operational records. The provider, meanwhile, may own the application code, proprietary algorithms, interface designs and certain internal technical assets.
Some information generated through use of the platform can be more complicated to classify.
The customer's rights depend on the data category, contract and applicable law. A statement such as "You own your data" is therefore less useful than a clear description of what the customer can access, export, reuse or request to be deleted.
Enterprise buyers should review the contract for export scope, permitted uses, exclusions, migration responsibilities and retention arrangements.
Personal information adds another layer. A business may have contractual rights relating to its customer records while also being required to protect personal data contained within those records.
For example, the GDPR provides individuals with a right to data portability in defined circumstances. That is distinct from a company's contractual ability to obtain an entire SaaS dataset.
The European Data Protection Board's guidance on data-subject rights explains the broader personal-data rights framework.
Legal ownership, contractual export rights and technical portability should be evaluated separately rather than treated as interchangeable concepts.
How the EU Data Act Changes the SaaS Portability Conversation
Enterprise procurement teams are also paying greater attention to data portability because of regulatory developments.
The EU Data Act, which began applying on 12 September 2025, includes provisions intended to reduce barriers when customers switch between covered data-processing services.
According to the European Commission's explanation of the Data Act, the relevant requirements can include contractual transparency, open interfaces and access to exportable information in commonly used, machine-readable formats.
The rules distinguish customer-generated input, output and relevant metadata from certain provider intellectual property and trade secrets.
They also contain specific qualifications.
Under Article 31, certain custom-built services may be exempt from particular switching obligations when the statutory conditions are satisfied. Limited-period, non-production testing services have a separate exemption. Providers must assess which obligations apply to their actual offering.
The legislation also schedules the elimination of applicable switching charges from 12 January 2027. That does not mean all termination penalties or independently agreed services are automatically prohibited.
These provisions are relevant to SaaS providers operating within the legislation's scope, including providers outside the EU where the applicable rules reach their services.
They are not a universal requirement for every SaaS contract in India or elsewhere.
For founders planning enterprise SaaS products, the practical response is to define export capabilities and switching arrangements early, then obtain jurisdiction-specific legal advice where required.
Technical portability is valuable in its own right, but an Export feature alone does not establish regulatory compliance.
A Backup Is Not the Same as a Customer Export
The enterprise buyer now asks whether the platform's regular backups could be used if an export fails.
Backups are essential for operational recovery, but they serve a different purpose.
A disaster-recovery backup may contain the application's complete database, configuration and information belonging to multiple customers. Restoring it may also require a specific software version and infrastructure.
That isn't necessarily something the provider can safely hand to an individual customer.
A customer export should contain the agreed information relating to that customer, without exposing other tenants' data.
A migration is another step again. The receiving system may need to transform fields, adapt workflows and map records into a different structure.
Even when an export contains every agreed record, the new application may not offer equivalent features.
A reliable portability plan recognises these differences.
For the supplier-management customer, retrieving invoice records is one task. Making those records work within a replacement procurement platform may require additional migration development and validation.
That work should be discussed before the transition begins.
What Happens to Customer Data After the Contract Ends?
Offboarding is often overlooked during product development because the immediate focus is on acquiring and retaining customers.
Yet the end of a SaaS relationship can involve several operational steps.
The customer may need to export its records, verify completeness and transfer information into another application. The provider must protect that data during the process and apply the agreed access, retention and deletion arrangements.
For the supplier-management platform, an offboarding request could begin with an authorised administrator selecting the required export scope.
The system prepares the package and records its completion status. Once the customer has retrieved and validated the information, access can be closed according to the contract.
The agreement should explain relevant timelines, responsibilities and assistance arrangements.
Data Deletion Requires More Than Closing an Account
After termination, the customer will also want to know what remains in the provider's systems.
Deleting an account from the application interface does not necessarily erase its records from backups, operational logs or systems subject to retention obligations.
A defensible deletion process distinguishes live application data from backup copies and legitimately retained records.
Customers should be told what is deleted, what may be retained, why it remains and when the relevant retention period ends.
Audit logs may record who authorised an export, when it was prepared, whether it completed successfully and whether errors occurred.
Those logs should provide accountability without unnecessarily retaining the exported sensitive information itself.
A deletion confirmation should describe what has actually happened, not make broader claims about backups or retained records that cannot yet be verified.
The SaaS Data Portability Checklist
Before approving a SaaS product for enterprise use, buyers and development teams should review the areas that could create serious difficulties during a future exit.
The following checklist separates critical requirements from those that may depend on the customer's operating model.
| Priority | Portability Requirement | What to Verify |
|---|---|---|
| Critical | Data scope and contractual rights | Which records can the customer retrieve, and what is excluded? |
| Critical | Export completeness | Are required records and historical information included? |
| Critical | Security and tenant isolation | Can only authorised users export the correct customer's information? |
| Critical | Usable formats | Can the customer access data in documented, machine-readable formats? |
| High | Record relationships | Are identifiers and links between related records preserved? |
| High | Files and attachments | Are required documents included and traceable to their records? |
| High | Offboarding arrangements | Are timelines, responsibilities and applicable charges clear? |
| High | Deletion and retention | What remains after termination, and for how long? |
| High | Auditability | Can export completion, failures and access be verified? |
| Conditional | API-based transfer | Is ongoing or staged data synchronisation required? |
| Conditional | Migration support | Does the destination system need mapping or transformation assistance? |
| Conditional | Specialised export requirements | Are industry-specific formats or retention obligations involved? |
This is an independent procurement and architecture checklist, not an official compliance certification.
For some customers, bulk export may be sufficient. Others may need controlled API access, detailed historical records or an extended migration period.
The requirements should match the customer's business needs and relevant contractual obligations.
Test the Export Before Promising That Customers Can Leave
Return to the hypothetical procurement platform.
The development team has prepared an export package and documented how its records relate to one another.
Now it needs to prove that the process works.
Suppose a test tenant contains 10,000 invoices, 2,400 purchase orders and several hundred attachments. The team generates an export and compares it with the original dataset.
The invoice file contains 9,970 records.
Rather than declaring the export successful because the download completed, the team investigates the missing 30 records.
The difference could come from an intended filter, a processing failure or an error in how the export handles pagination.
Until the team knows which explanation is correct, the package cannot be treated as complete.
A Practical Export Acceptance Test
The test should verify record counts, required fields, relationship integrity and attachment availability.
It should also confirm that dates, amounts, statuses and identifiers retain their intended meaning after export.
Checksums can help identify unexpected changes to files during transfer. A manifest can record missing items and processing errors, allowing those issues to be resolved before handover.
The team should also test access restrictions using appropriately isolated test tenants.
A successful export must not include unauthorised records from another customer.
Finally, a representative sample of the exported data should be read or imported in a separate validation environment.
This doesn't prove that every destination SaaS platform can reproduce all the original functionality. It does provide evidence that the agreed information is present, interpretable and usable for the intended transfer.
That distinction is valuable during enterprise procurement.
Instead of asking the buyer to trust a feature description, the provider can demonstrate the export process against defined acceptance criteria.
Build Data Portability Into the Product Before It Becomes Expensive
Retrofitting data portability after years of SaaS development can create unnecessary complications.
The platform may have undocumented record relationships, attachments stored separately from their metadata, or internal identifiers that are difficult to preserve outside the application.
These problems are easier to address when the data model and tenant boundaries are being designed.
A SaaS product team should define which records belong to each customer, how records relate to one another and which information must remain accessible over time.
It should also consider export permissions, historical data, deletion policies and likely integration requirements.
That doesn't mean every startup needs a complex enterprise migration system in its first product release.
It means early architecture decisions should leave room for a clear and secure exit process as the product matures.
For SaaS founders preparing to serve enterprise customers, Aquarious Technology's SaaS product development and architecture services provide a relevant starting point for evaluating data models, integrations, tenant isolation and long-term product requirements.
A development partner should be able to explain how those architectural choices affect customer rights, technical operations and future migration needs.
A strong product design is not just about supporting growth. It should also avoid making basic customer data retrieval unnecessarily difficult.
Enterprise Trust Includes Knowing How to Leave
The enterprise buyer in our example liked the SaaS platform. Its features met the business requirements, and the commercial proposal was reasonable.
The hesitation came from uncertainty about what would happen to years of operational data if the company changed systems.
A clear export specification, documented ownership terms and a tested offboarding process would give that buyer a better basis for making the decision.
Portability doesn't make switching effortless. Different software platforms use different data structures and may require significant migration work.
But customers should be able to understand what information they can retrieve, how it will be delivered and where the limitations lie.
For SaaS providers, those capabilities can strengthen confidence without removing the value of the product itself.
A good SaaS platform should give customers reasons to stay because the software works for them, not because their business records are too difficult to take elsewhere.