
The software has been running smoothly for six months. The operations team uses it to track purchase requests, monitor pending work and keep records that previously lived in spreadsheets.
The department head is pleased with the result. Requests are easier to find, employees spend less time following up, and managers can see what needs attention without calling several people.
Now the company wants Finance, Procurement and Warehouse teams to start using the same application.
That seems like a reasonable next step. The software already works, and most employees deal with the same purchase requests at different stages.
But the first joint meeting reveals a problem.
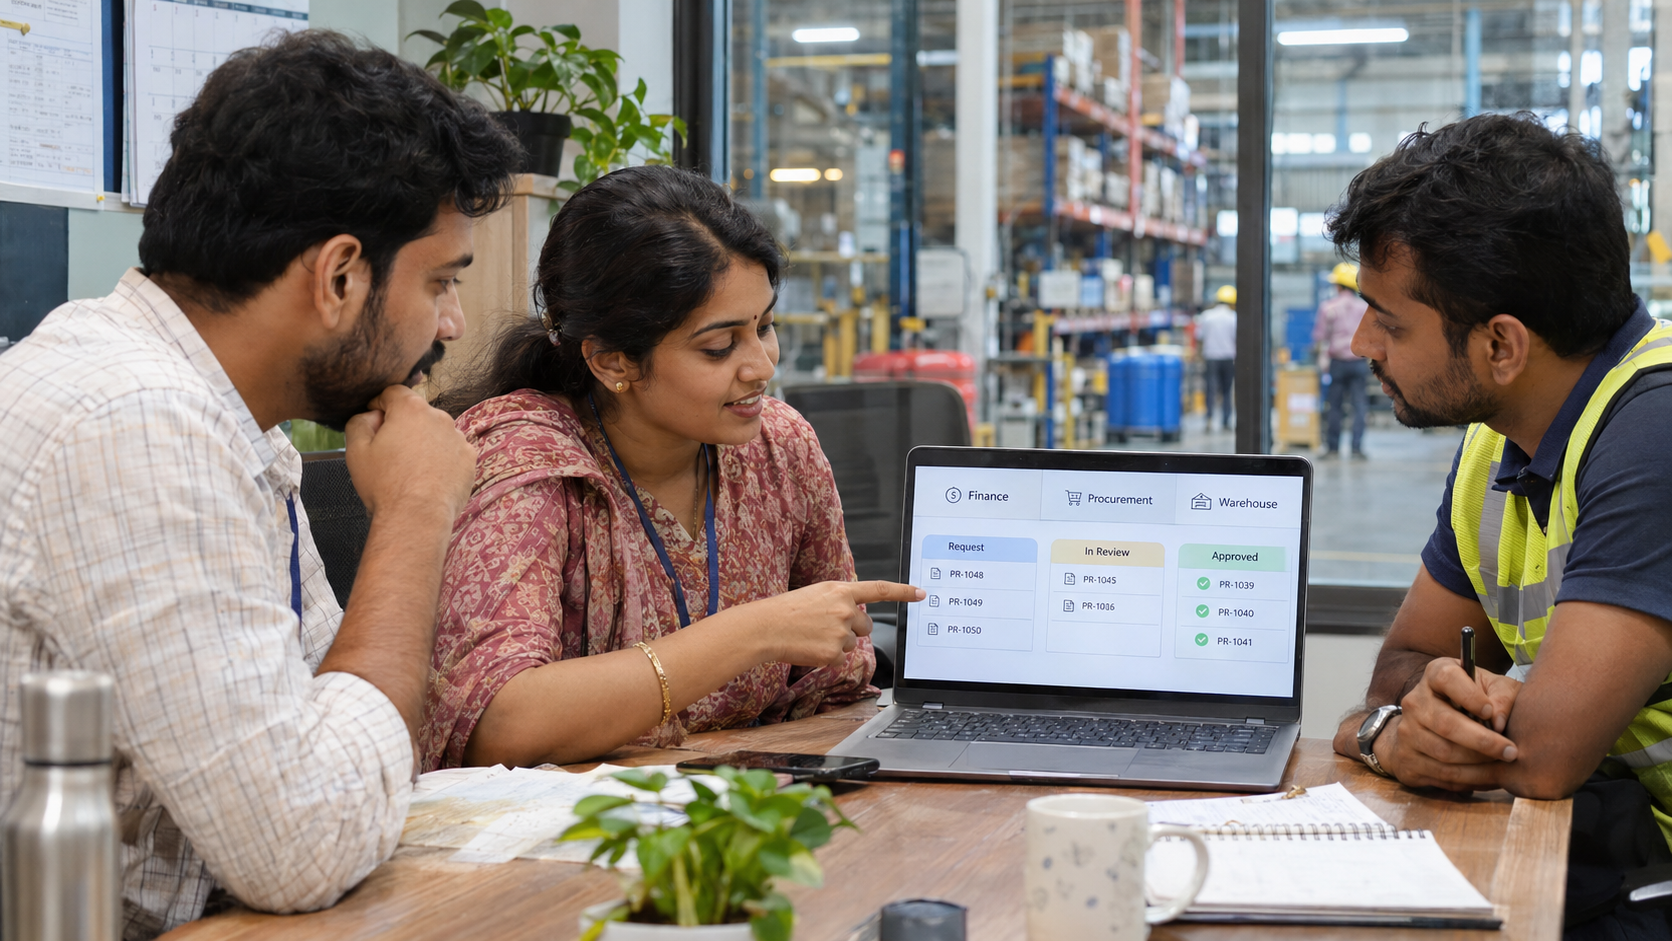
Procurement wants to edit supplier details. Finance needs to check budgets and approve certain expenses. Warehouse employees must confirm deliveries, while Operations wants to retain control over the original requests. Each department also has its own definition of when a request is complete.
The software was designed around one team's way of working. Expanding it across the business requires more than creating additional user accounts.
Scaling custom software across departments means adapting its data structure, access permissions, business rules and workflows so multiple teams can work on connected processes without losing accountability or creating conflicting records.
The application may already be technically capable of supporting hundreds of users. The more difficult question is whether it can support hundreds of users doing different jobs.
The business scenario used throughout this article is illustrative, not a documented Aquarious client project.
The First Department Didn't Need to Solve Everyone's Problems
Consider a hypothetical manufacturing company that developed a custom application for its Operations department.
The original requirement was straightforward. Employees needed to raise purchase requests, attach supporting documents and monitor whether each request had been approved.
Operations managers could approve requests and update their status. Everyone involved worked within a reasonably consistent process.
Once the application proved useful, management decided to extend it to other departments.
This changed the nature of the product.
Procurement needed to turn approved requests into supplier orders. Finance needed to verify expenditure against budgets. Warehouse employees had to confirm that the delivered quantities matched the purchase orders.
The business process was no longer confined to one department. A single request could now move through several teams, each responsible for a different decision.
A developer could add more screens and user accounts, but that wouldn't necessarily solve the underlying problem. The application needed a shared understanding of the process and a clear division of responsibility.
That is where cross-department software planning begins.
Shared Data Doesn't Mean Everyone Should Have the Same Access
When several teams use one application, they often need access to information about the same transaction.
However, their permissions shouldn't automatically be identical.
Procurement may need to change a supplier's contact details, while Finance may only need to view them. Warehouse staff might need to confirm received quantities but should not be able to alter the approved purchase amount.
The application must distinguish between a user's identity, their organizational responsibilities and the actions they are allowed to perform.
Role-Based Access Needs to Reflect Business Decisions
A role-based access control model can provide a useful starting point.
For the manufacturing company, the software might distinguish Operations Requesters, Procurement Officers, Finance Approvers and Warehouse Receivers.
But roles alone may not be enough.
A Finance Approver might only be authorized to approve expenditure for a particular division or within a specified financial limit. An Operations Manager may be allowed to view requests from their own department but not confidential records from another business unit.
Microsoft's role-based access control guidance explains how application roles can be used to manage permissions. More granular authorization may also depend on the specific record and business context.
For a cross-department application, the technical team should define permissions at the action and record levels, not just decide which menu items each role can see.
An employee who cannot see an approval button should also be unable to perform the approval through a direct API request.
The OWASP Authorization Cheat Sheet provides additional guidance on enforcing access consistently and avoiding unauthorized operations.
Permission design becomes especially important when the application handles financial information, employee details or commercially sensitive transactions.
One Purchase Request, Several Different Versions of the Truth
The manufacturing company encounters another issue during its planned expansion.
Operations marks a purchase request as approved. Procurement converts it into a purchase order, but the supplier later confirms that part of the order will be delayed.
Finance sees the original approved amount. The warehouse sees only the goods that have already arrived.
Each team is looking at a different stage of the same transaction.
If every department maintains its own independent version of the record, the business may end up with conflicting information.
The software needs a defined data model that connects requests, orders, deliveries and financial approvals without treating them as interchangeable records.
Decide Which Team Owns Each Business Record
For example, Operations may own the initial purchase requirement. Procurement may own supplier negotiations and purchase orders. Finance may own budget approval and payment authorization, while Warehouse owns goods-received confirmations.
These are business responsibilities that should influence the application's data model and authorization rules.
The goal isn't to create an entirely separate database for every department. It's to establish which information is authoritative, who may change it and how other teams receive those updates.
Martin Fowler's discussion of integration databases highlights how shared data structures can tightly couple systems when different applications depend on the same records.
A unified custom software application may legitimately use shared storage, but its internal ownership rules still need to be explicit.
Otherwise, a change that helps one department could unintentionally disrupt another team's workflow or reporting.
Different Approval Rules Can Break an Otherwise Working System
The original Operations application allowed a department manager to approve purchase requests.
That worked until Finance joined the process.
Finance now requires an additional approval when expenditure exceeds a particular threshold. Procurement needs supplier verification before issuing certain orders, while Warehouse should only record receipt after an order has been released.
A single generic approval field cannot accurately describe all these decisions.
Consider an illustrative purchase request worth ₹1.8 lakh.
Operations has approved the business need, but Finance has not yet confirmed the expenditure. If the system simply records the request as "Approved," Procurement might interpret that status as permission to place the order.
The software needs to distinguish approval of the requirement from authorization to spend.
Model the Workflow Around Business Events
A clearer workflow could move through distinct stages:
| Workflow stage | Responsible team | Meaning |
|---|---|---|
| Request submitted | Operations | Purchase requirement recorded |
| Business need approved | Operations Manager | Requirement is justified |
| Budget authorized | Finance | Expenditure is permitted |
| Supplier selected | Procurement | Commercial terms established |
| Purchase order issued | Procurement | Authorized order created |
| Goods received | Warehouse | Delivery details recorded |
| Invoice cleared | Finance | Relevant financial checks completed |
This is an illustrative workflow. Real approval stages, delegation rules and financial limits must be agreed with the business.
The important design decision is that each stage has a defined meaning and an authorized owner.
A workflow should also address exceptions. Suppliers may deliver only part of an order, requests can be rejected, and authorized employees may need to delegate approvals during an absence.
If these cases are ignored, employees may eventually bypass the application and return to email or spreadsheets to finish their work.
Reporting Becomes Harder When Every Department Defines Success Differently
The management team wants a single dashboard showing the status of all purchase requests.
Operations considers a request complete when the department's need has been approved. Procurement considers its task complete when the purchase order has been issued. Warehouse considers its work complete after receiving the goods.
All three teams are using the word complete, but they mean different things.
A consolidated report can become misleading unless the application preserves the distinction.
The solution is to define shared business events and reporting rules.
For example, the dashboard could show the number of requests awaiting budget approval, orders awaiting supplier confirmation and deliveries with outstanding quantities.
Management can then understand where work is delayed without forcing every department into one status definition.
Reporting should also preserve historical information. If a request was approved on Monday and an order issued on Thursday, the application should be able to distinguish those events rather than replace one status with another and lose the timeline.
A useful cross-department system makes the business process visible without erasing the responsibilities of the people involved.
Integrations Become More Important as More Teams Join
The original application might have operated independently because Operations was its only user.
Once Finance and Procurement become involved, the software may need information from accounting, inventory or supplier-management systems.
These integrations create new decisions.
Should the custom software maintain its own supplier records, or retrieve them from an existing system? Which application owns purchase-order numbers? What happens if an accounting integration fails after the purchase order has already been created?
Copying data between systems without clear ownership can produce duplicate records and inconsistent reports.
Where applications exchange business events, the technical design should also account for retries and duplicate processing. A temporary network failure shouldn't create two purchase orders because the same integration request was submitted twice.
The team should define the expected behaviour when a connected service is unavailable.
Sometimes an operation can remain pending until the integration recovers. In other cases, the user may need immediate confirmation from the authoritative system before continuing.
These decisions are part of cross-department software architecture, not simply tasks to complete after development.
The Cross-Department Software Readiness Matrix
Before extending a working application, business leaders and technical teams need a shared way to assess whether it can support the next department.
The following matrix identifies the decisions that most often affect cross-department adoption.
| Readiness area | Key requirement | Evidence of readiness |
|---|---|---|
| Department responsibilities | Each team has defined ownership of relevant activities | Approved responsibility map |
| User permissions | Actions and records are restricted appropriately | Role and record-level access tests |
| Shared data | Authoritative records and update permissions are defined | Data ownership documentation |
| Workflow rules | Approval stages and exceptions are agreed | Tested end-to-end workflow |
| Integrations | Connected systems have clear responsibilities | Integration and failure-recovery tests |
| Reporting | Business terms and status definitions are consistent | Reconciled cross-department reports |
| Audit history | Important decisions and changes remain traceable | Reviewable event history |
| Scalability | Expected users and workload have been assessed | Performance-test evidence |
| Training and support | Each department understands its tasks | Role-based training and support plan |
| Rollout and rollback | Expansion can be controlled and problems contained | Signed-off pilot and recovery plan |
Each area can be classified as Ready, Partially Ready or Not Ready.
For example, the application may already support the expected number of users but still lack the permission controls needed by Finance.
That should be recorded as a business-readiness gap rather than hidden inside a general statement that the software is scalable.
The purpose of the matrix is to identify which requirements must be resolved before more teams depend on the application.
Don't Roll Out to Every Department on the Same Day
Once the software has been adapted, management may want all departments to begin using it immediately.
That can create unnecessary operational risk.
A controlled rollout allows the business to validate one complete cross-department process before extending the application more widely.
The manufacturing company could begin with a small group of purchase requests involving Operations, Procurement and Finance.
The pilot should include ordinary cases and predictable exceptions, such as a rejected budget approval or a purchase order requiring revision.
Warehouse participation can follow when the earlier stages produce reliable records and the receiving workflow is ready.
Test the Entire Business Journey
A useful acceptance test should follow a purchase request from submission through the relevant approvals, purchase-order creation and delivery confirmation.
The team should verify that permissions remain correct at every stage and that reports reflect the same underlying events.
It should also test what happens when an approver is absent, an integration fails or a user attempts an unauthorized status change.
The pilot should use agreed success criteria. For example, the business may require all tested purchase requests to retain complete approval histories and reconcile correctly with purchase-order records.
These are acceptance conditions, not claims about a verified implementation.
Only after the workflow performs reliably should the organization extend the system to additional users, departments or locations.
More Users Don't Automatically Mean the Software Is Ready to Scale
A system can handle a larger user count and still be unsuitable for wider business adoption.
Technical capacity is only one part of scaling custom software.
The application also needs to accommodate more complex permissions, shared records and different operational responsibilities.
For some businesses, the existing software may be flexible enough to support these changes through configuration and carefully designed extensions.
For others, the original data model or application architecture may need substantial changes before expansion is practical.
The team should evaluate both options rather than assume that every new departmental requirement needs a separate module.
Adding features without reviewing the underlying workflow can create a larger application that is harder to maintain.
A more useful approach is to understand where the business process genuinely needs to be shared and where departments require different rules.
Turning Departmental Software Into a Business-Wide System
Expanding custom software is easier when the organization treats it as a business-process initiative rather than a simple user rollout.
Operations, Finance, Procurement and Warehouse should agree on what information they share, which team is responsible for each decision and how exceptions will be handled.
The development team can then translate those requirements into authorization rules, workflow logic, data structures and integration behaviour.
For businesses considering broader software adoption, Aquarious Technology's custom software development for connected business workflows provides a relevant starting point for evaluating enterprise applications, integrations and requirements that extend across departments.
The next useful step is a structured discovery exercise covering business responsibilities, current systems, approval dependencies and the expected rollout sequence.
That creates a stronger foundation than starting with a list of new screens or additional user licences.
Frequently Asked Questions About Scaling Custom Software
Yes, provided its architecture and business rules can accommodate additional teams. Expansion may require new permission controls, shared data structures, approval workflows, integrations and reporting capabilities. The development team should assess these requirements before rollout rather than assume the application is ready simply because it already performs well for one department.
The main challenges often involve conflicting business rules, inconsistent record definitions and unclear ownership of shared information. For example, Finance and Procurement may both use a purchase-order record but have different responsibilities for approving and changing it. A successful integration needs agreed data ownership, appropriate authorization and clear handling of errors between connected systems.
No. Existing software may be extended through configuration changes, additional workflows, improved permissions or carefully planned integrations. More substantial architectural changes may be required when the original data model, security design or application structure cannot support the new requirements. The decision should follow a technical assessment and a review of the business workflows.
Businesses should define permissions according to job responsibilities and the specific records or actions involved. Role-based access can provide a foundation, but some decisions also require conditions such as department ownership, financial approval limits or record status. Access rules should be enforced by the application backend and tested against unauthorized requests.
Businesses should examine the provider's requirements-discovery process, enterprise application experience, integration capabilities, security practices and approach to testing. For multi-department projects, it is especially useful to ask how the provider handles conflicting approval rules, shared data ownership and phased deployment. Verified project examples and clearly defined acceptance criteria provide stronger evidence than general promises of scalability.
Software That Works Across the Business Needs Shared Decisions
The manufacturing company's original application was successful because it solved a clear problem for Operations.
Expanding it introduced a different challenge. Several departments needed to work on connected transactions without sharing identical responsibilities or rules.
The software could support that process, but only after the business clarified how its teams should work together.
A successful expansion therefore depends on more than performance or the number of employees who can log in.
It requires consistent data ownership, appropriate permissions, clear approval stages and a rollout that allows problems to be identified before they affect the entire organization.
Custom software is ready to grow across departments when it can support different teams working on the same business process without creating conflicting information or unclear accountability.